The most expensive lock in the world is useless when nobody notices how many people are walking through the door.
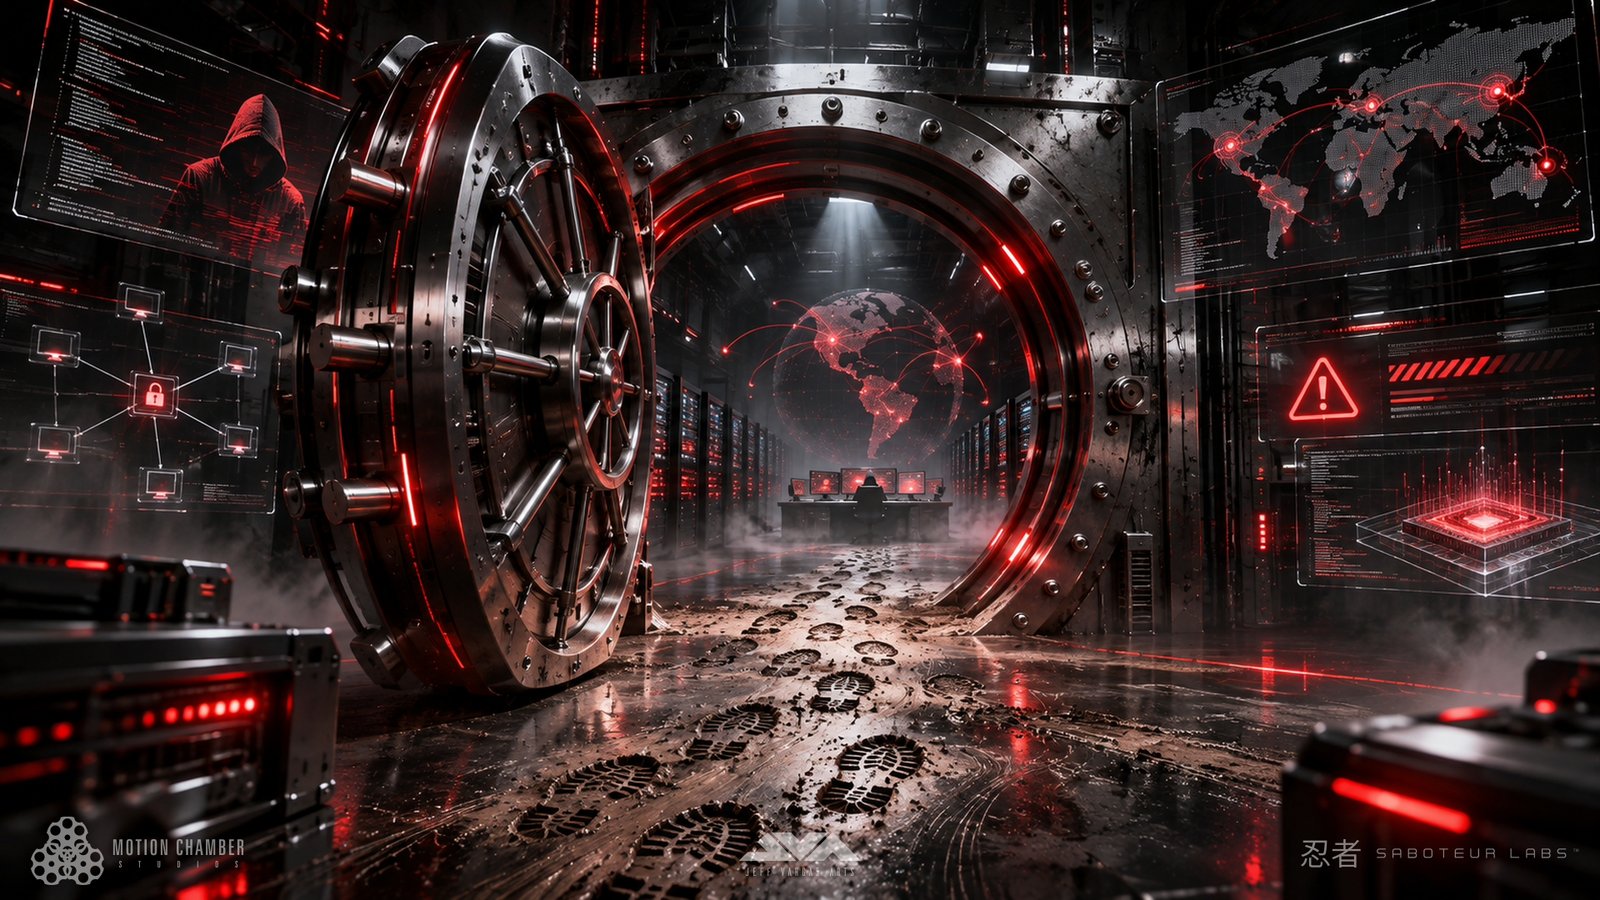
There is something profoundly unsettling about an open vault.
Not because the door has failed. Not because the hinges have been destroyed or the locking mechanism defeated.
But because the floor is covered in footprints.
Dozens of them. Overlapping. Crossing in different directions. Mud dragged across polished surfaces. Scuff marks accumulating where people have clearly been coming and going for some time.
This wasn’t a single intrusion.
This was traffic.
And somewhere, an extraordinarily expensive security system has been confidently reporting that everything is fine.
THE ILLUSION OF THE LOCK
The imagery is familiar. Darkened rooms. Glowing terminals. Global network maps. A mysterious figure in a hoodie, because apparently cybersecurity regulations require at least one.
But the most revealing feature of this scene isn’t the hacker.
It’s the evidence that nobody was watching the doorway.
Organizations invest enormous resources in protecting digital infrastructure. Firewalls, intrusion detection, encryption, authentication systems, behavioral analytics, and increasingly sophisticated monitoring platforms.
All necessary. All valuable.
And none of them particularly useful if their underlying assumptions are wrong.
A contractor retains access long after a project ends.
An integration receives permissions it never needed.
An old application remains exposed because disconnecting it might break something important.
A service account quietly acquires administrative privileges.
A security exception becomes permanent because nobody remembers who approved it.
Individually, these decisions can appear reasonable.
Collectively, they can turn a secure environment into a remarkably efficient public entrance.
EVERYONE HAS A KEY
The modern cybersecurity problem isn’t simply keeping malicious actors outside a perimeter.
It’s understanding where the perimeter actually exists.
Applications connect to other applications. Employees work from multiple devices and locations. Vendors require temporary access. Automated services exchange information continuously. Cloud infrastructure makes resources available from almost anywhere.
The network is no longer a fortress surrounded by a moat.
It’s an interconnected city.
And every connection potentially introduces another doorway.
Attackers exploit vulnerabilities, steal credentials, compromise trusted systems, and take advantage of relationships that defenders have legitimate reasons to maintain.
The uncomfortable reality is that unauthorized activity can sometimes look remarkably similar to authorized activity.
Especially when the credentials are valid.
Especially when the system has been configured to trust the source.
Especially when nobody has revisited that trust in three years.
THE FOOTPRINT PROBLEM
A successful intrusion isn’t necessarily defined by spectacular technical sophistication.
Sometimes the initial compromise is relatively simple.
The sophistication comes afterward.
Discovering what is accessible. Finding connected systems. Escalating privileges. Moving between environments. Extracting information. Maintaining access.
And, ideally for the attacker, doing all of it without attracting attention.
This is why the footprints matter.
Not just the first set leading through the entrance.
All of them.
The paths taken. The areas visited. The repeated crossings. The activity that should have been unusual but gradually became indistinguishable from ordinary operations.
Security isn’t simply a question of whether the door can be locked.
It’s whether the organization understands what happens after someone passes through it.
Who entered?
What did they access?
Why did they have permission?
What changed?
And how long did it take anyone to notice?
THE MACHINE SAYS EVERYTHING IS FINE
The growing sophistication of artificial intelligence adds another dimension.
Automated systems can help defenders correlate events, identify anomalies, prioritize vulnerabilities, and investigate suspicious behavior across enormous volumes of information.
Those same capabilities can also assist attackers in identifying weaknesses, accelerating reconnaissance, and operating at greater scale.
The result isn’t necessarily a world where every attack becomes unstoppable.
It’s one where speed, visibility, and the quality of security decisions matter enormously.
A dashboard filled with reassuring green indicators is not proof of safety.
It is proof that the conditions being measured currently satisfy the rules someone configured.
Whether those rules are still meaningful is a different question.
And whether anyone is asking that question may be the most important issue of all.
CLOSE THE DOOR. THEN CHECK THE FLOOR.
Good security architecture requires more than increasingly impressive barriers.
It requires limited privileges, continuously reviewed access, timely updates, meaningful monitoring, clear ownership, and the ability to respond when an assumption proves false.
It requires knowing which doors exist.
And acknowledging that some of them were opened deliberately, for perfectly legitimate business reasons, before anyone realized what they exposed.
The goal isn’t absolute invulnerability.
No credible system can promise that.
The goal is reducing unnecessary exposure, detecting suspicious activity, limiting the damage when controls fail, and recovering without discovering that the entire organization depended on one forgotten administrator account.
Look again at the vault.
The door is enormous. The engineering is magnificent. The locking mechanism is an industrial masterpiece.
And the floor looks like the entrance to a shopping mall.
Perhaps the most important cybersecurity question isn’t:
How did they get in?
It’s:
How long were they coming and going before anybody bothered to look?